




Doctors Applies to: Denmark
Encrypted exchange of medical reports
Send reports to patients and colleagues and request documents – encrypted, no patient account needed.
- Developed & operated in Germany
- End-to-end encrypted
- Contractual confidentiality obligations
- Signed proofs of delivery
What your professional rules require
Patients are entitled to have health professionals keep their health and other confidential information secret (sundhedslovens kapitel 9, Danish Health Act).
In Datatilsynet’s view, health data sent by email over the internet should normally be encrypted. Notifications contain no file names; choose file names and labels that do not refer to patients.
How TEPHIA SECURE meets them
Contractual confidentiality
In clause 5b, our data processing agreement commits us to confidentiality, limits access to what the service requires and binds everyone involved in writing. You conclude it electronically and receive a copy as a PDF.
State of the art
AES-256-GCM encryption in the sender’s browser, with the key derived from the password using Argon2id. The server holds no key and cannot read the contents. Email notifications contain no file names, and the PDF proof of delivery is attached only if you choose.
No account needed for recipients
Patients do not need an account. Patients and colleagues can send you documents through an upload box, with the same protection and the same proof of delivery.
Verifiable proof of delivery
Each entry is cryptographically chained to the previous one. The proof of delivery is a signed PDF/A with a timestamp from an independent time-stamping authority.
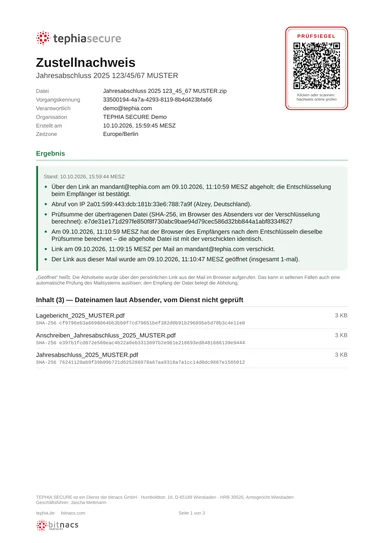
How your proofs are secured
| In every planSignature with our certificate | Add-on · coming soonQualified electronic seal | |
|---|---|---|
| Any change to the PDF invalidates the signature | included | included |
| Timestamp from an independent authority | included | included |
| Hash chain with daily chain seal | included | included |
| Checksum (SHA-256) of every file, confirmed by the recipient | included | included |
| Verifiable online, without an account | included | included |
| Display in Adobe Reader | “Validity unknown”1 | Valid |
| Legal presumption of authenticity (Art. 35(2) eIDAS) | not included | included |
| Useful for | Your records, clients | Courts, authorities, the other party |
1 Not an error: our certificate is not on the EU trust list that Reader recognises. You can check integrity online or using the certificate fingerprint.
- Signature: any change is detected
- Timestamp from an independent authority
- Hash chain with daily chain seal
- Checksum of every file, confirmed by the recipient
- Verifiable online, without an account
- Adobe Reader shows “Valid” instead of “Validity unknown”
- Legal presumption of authenticity (Art. 35(2) eIDAS)
- Useful for courts, authorities, the other party
There is no certification of services like this by a professional body, and carefully selecting a service provider remains your responsibility under your professional rules.
The information on the legal position on this page is general information, without any warranty as to completeness or currency, and does not constitute legal advice. Only our contracts are binding.